The encryption architecture.
Private in transit.
Protected at rest.
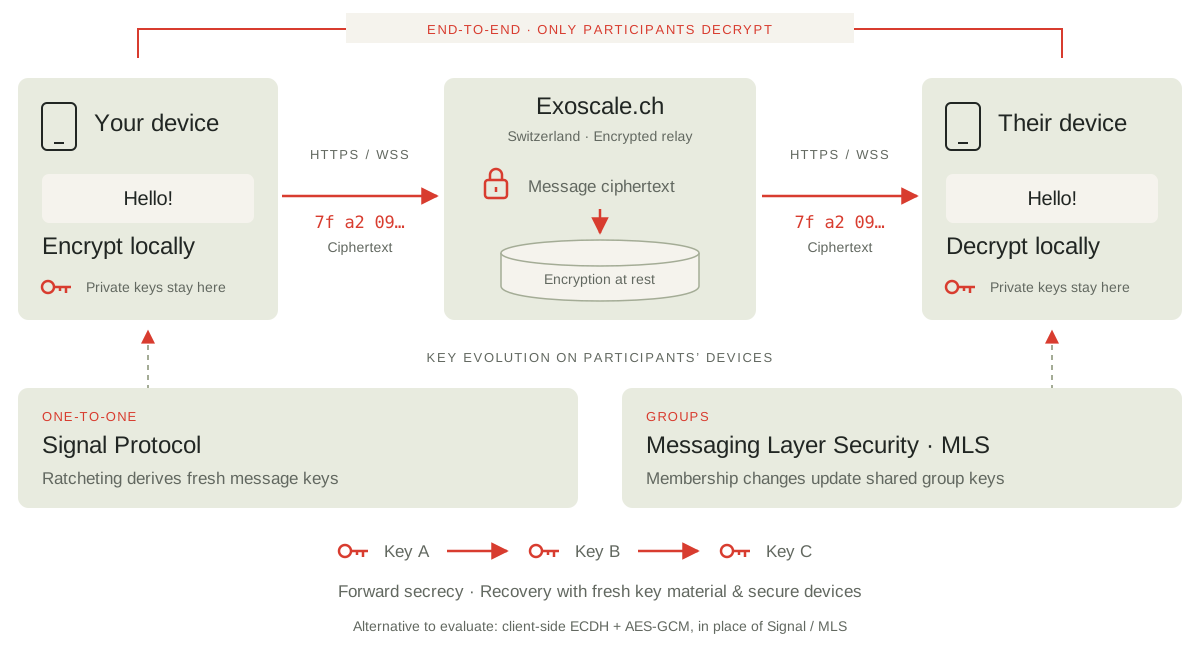
End-to-end encryption keeps the conversation between you and your recipients. Encryption at rest adds protection for stored data.
Only the people in the conversation
Messages are encrypted before leaving your device. Exoscale.ch relays and stores ciphertext; only recipients decrypt the message body.
Another layer for storage
A separate storage-encryption layer protects the ciphertext on disk. HTTPS and secure WebSockets (WSS) also encrypt the network connection.
Exoscale.ch · Switzerland
Blind relay · Ciphertext only · Encryption at rest
Fresh keys.
Stronger conversations.
The encryption brief sets out protocols for private messages and group conversations, with keys that evolve over time.
Signal Protocol · One-to-one
Cryptographic ratcheting derives fresh message keys. Forward secrecy protects earlier messages; post-compromise security supports recovery after a key compromise.
Messaging Layer Security · Groups
MLS (IETF RFC 9420) establishes shared group keys and updates them as membership changes, supporting forward secrecy and post-compromise security.
A new key as the conversation moves.
Ratcheting limits how much a compromised key can reveal. Recovery depends on fresh key material and secure devices.
Alternative in the brief
Client-side ECDH key exchange + AES-GCM authenticated encryption. This is an alternative to evaluate, rather than an extra protocol layered onto Signal or MLS.
Protocol design from the Peak.ch brief · Signal specification · MLS standard
Your private keys.
Stay with you.
The server is a directory, a relay, and an encrypted storage locker. Private message keys belong on your devices.
Generated and protected locally
Use OS-protected key storage on mobile devices, such as iOS Keychain or Android Keystore, with hardware backing where available. The locked-down CEF app also needs protected key storage. Its per-user mTLS key authenticates access separately from message encryption.
Public keys for delivery
The server distributes public keys and one-time pre-keys so people can establish encrypted sessions. It never receives private message keys.
On Exoscale.ch in Switzerland
Public keys & pre-keys
Encrypted message bodies
Encrypted storage
Secure, real-time delivery
WSS carries live messages. HTTPS APIs handle SwissID sessions and public-key retrieval. Transport encryption adds protection around the end-to-end encrypted payload.
Encryption architecture from the Peak.ch brief.
Posts & changes.
Through the app.
To see posts and make changes, users need to use the peak.ch app.
A locked-down CEF browser
The app uses Chromium Embedded Framework (CEF), with a private key for mutual TLS (mTLS) that is different for each user.
“Global Public” is the browser exception
Only pages marked as “Global Public” can be seen by standard browsers, anywhere. Making changes requires the app.
Most
Restricted accessNeed app to view posts · make changesPublic
Open to anyone registeredNeed app to viewSwitzerland - Only
Standard browser access
“Global Public” pages onlyOpen from a standard browser, anywhere:
https://peak.ch#Noggeler_Guuggenmusig